Release Notes — April 2026

Release period: 2026-04-01 → 2026-04-30
April brings AI security front and center: discovery of AI agents, models, and MCP tools from cloud providers, the first AI Policies and guardrail alerting, and a major step forward for web application scanning (DAST) with AI-driven authentication. We also expanded reporting, hardened sensors, and shipped new deployment options.
Highlights
- AI discovery for agents, models, and MCP — Levo now automatically discovers AI agents, models, and MCP servers and tools from your traffic, including AWS Bedrock and Gemini, so your AI footprint is cataloged alongside your APIs.
- AI Policies and guardrail alerting (beta) — A new AI Gateway policy framework with guardrail alerts that capture prompt snippets, detection scores, model name, and MCP context, giving you visibility and control over AI usage.
- DAST gets smarter authentication — Web app scans now support AI-driven login and flexible auth strategies, with deployable scan runners and improved scan depth and fidelity to reduce false positives.
- Proof-based injection testing — New semantic, proof-based SQL and NoSQL injection detection delivers high-confidence findings with dramatically lower false positives.
- AWS ECS Fargate deployment — One-click deploy and enhanced installation scripts for running the Satellite and PCAP sensor on AWS ECS Fargate.
- Redesigned sign-in and dark mode — A refreshed authentication experience plus a new dark mode in the admin portal.
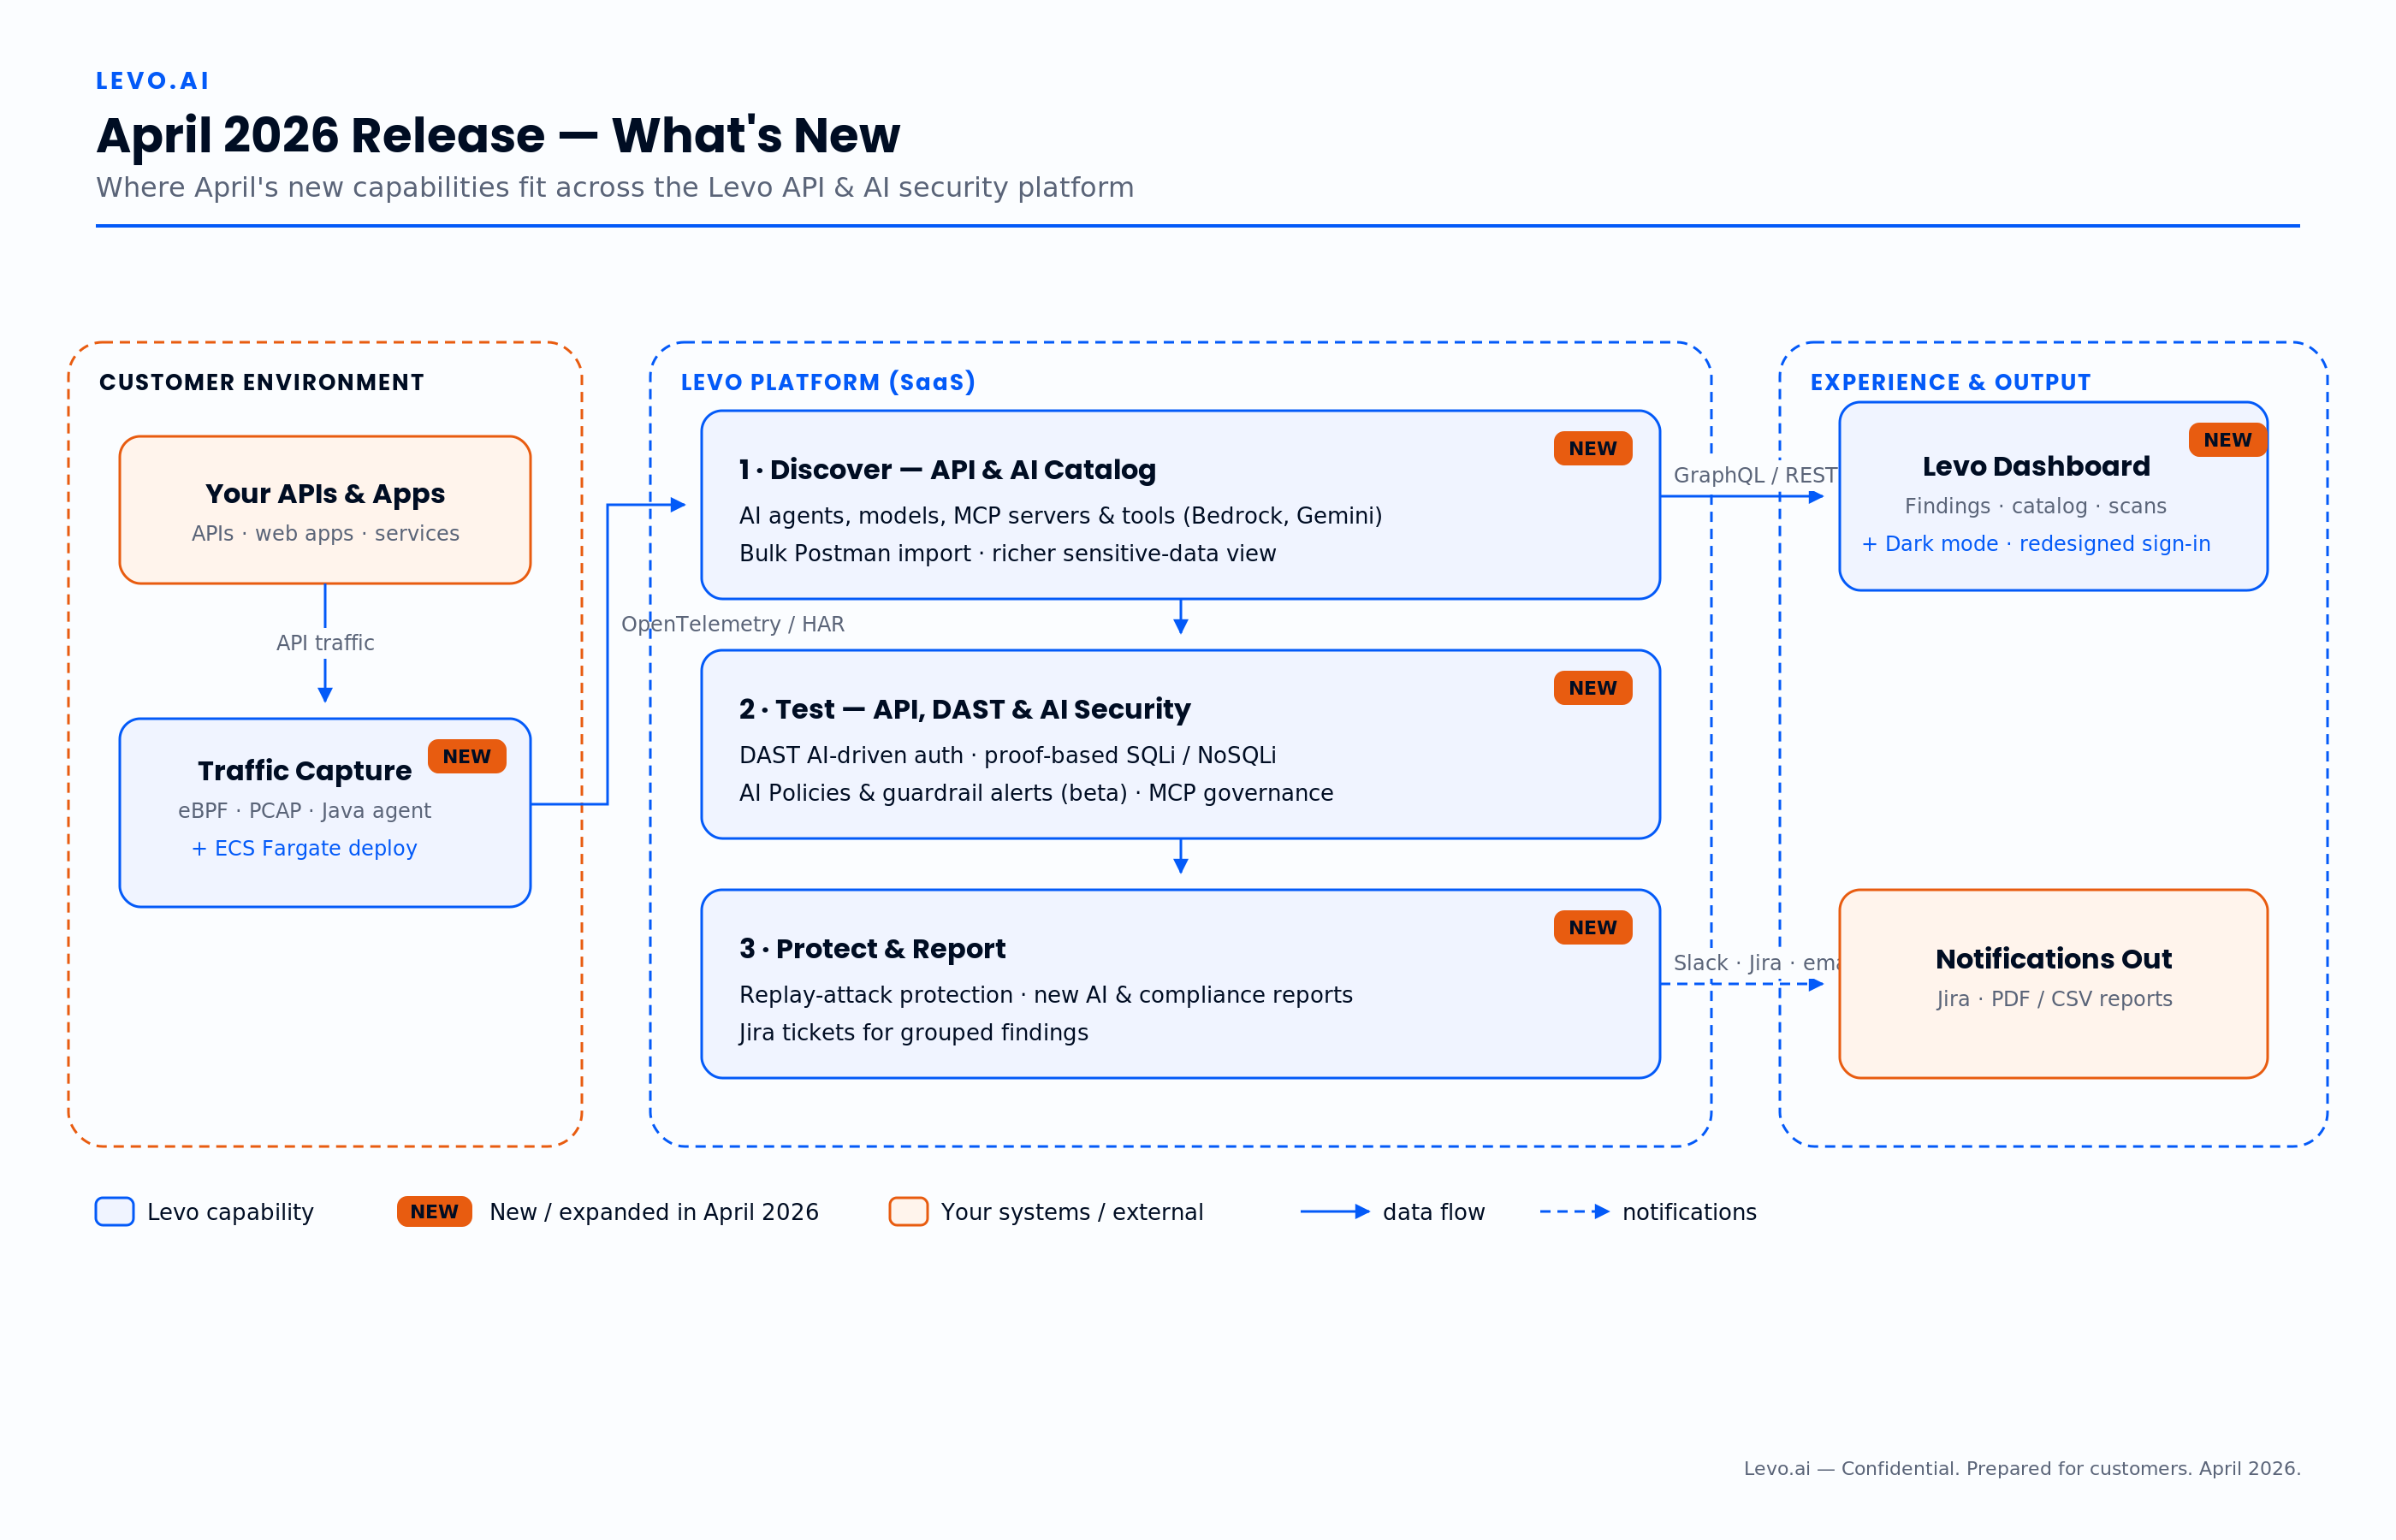
What's new at a glance. A one-page map of where April's additions land across the Levo API and AI security platform.
API Discovery & Cataloging
New Features
- Large and bulk Postman imports — Import large Postman collections in bulk, with normalized path segments to prevent duplicate endpoints.
- Discover APIs from .NET and C# source — Source-code scanning that surfaces APIs into your inventory now supports .NET and C#, finding endpoints that may not appear in live traffic.
- Filter endpoints by the time of the last trace received, and apply a global quick filter for all, external, or internal endpoints on the Auth Schemes view.
- Endpoint exports now cover zombie and inactive endpoints, with sensor export pagination.
Resolved Issues
- Trace-to-endpoint race conditions and duplicate endpoints from imports.
API Security Testing
New Features
- Proof-based SQL and NoSQL injection detection — New semantic, evidence-driven detection for SQLi and NoSQLi with very low false-positive rates.
- Improved assertions for CORS and injection attacks, and aggregated sub-technique assertions for mass-assignment testing.
Resolved Issues
- A SQLi union-canary false positive triggered by server input echo.
- A URL-parsing error.
Web Application Scanning (DAST)
New Features
- AI-driven authentication for scans — Web app scans support AI-assisted login, including extra steps for AI/LLM keys and advanced header fields; the feature is now out of beta.
- Deployable DAST scan runners — Run web app scans from deployable runners, with re-run and configurable scan depth.
- Endpoints are now segregated by source, with a "URLs by Source" tab, live scan metrics, and visibility into URLs pending in the queue.
- Smarter scanning that is tech-stack aware, plus improved detection for command injection, file upload, and stored XSS.
- "WebAppScan" is now consistently named "DAST Scan" across the product.
Resolved Issues
- Significant false positives and signal-quality issues across scanners.
- Scan timeouts are reported as cancelled.
AI Security
New Features
- AI Policies and AI Gateway policies (beta) — A new policy framework for governing AI usage, with expanded MCP governance policies. The feature is disabled by default while in beta.
- AI guardrail alerts — Guardrail alerts capture prompt snippets, detection scores, model name, and MCP context, with an alert detail drawer, export, and multi-select in the dashboard.
- Transparent TLS interception and MCP sidecar — The AI Gateway adds transparent TLS interception, sidecar injection (including Java sidecar support with TLS trust-store injection), and auto-configuration of TLS interception, enabling inline inspection of AI traffic.
- The gateway now buffers request bodies for man-in-the-middle inspection and adds a configuration to suppress noisy HTTP methods.
Resolved Issues
- Guardrail alerts are not isolated per tenant.
- Guardrail-related crash loops.
- Guardrail alerts are truncated.
AI Discovery
New Features
- Discover AI agents, models, MCP servers, and tools — Levo discovers AI agents, MCP servers, and MCP tools from AWS Bedrock tool configurations, and extracts model names from Bedrock and Gemini request paths.
- AI and MCP entities are now labeled in the endpoint TYPE column, and full LLM request bodies are forwarded for accurate agent and MCP entity discovery.
Resolved Issues
- AI trace ingestion for Bedrock fails on base64-prefixed streaming responses, large payloads, and paths containing colons.
- Pagination and sorting issues in the AI Models and AI Agents views.
Vulnerabilities & Findings
New Features
- Jira tickets for grouped findings — Create a Jira ticket linked to multiple endpoints directly from grouped findings, and filter findings by whether they have a Jira ticket.
- Merged category options in vulnerability filters and a stats API that updates as you apply findings filters.
Resolved Issues
- Jira ticket and delete icons are sized incorrectly in Findings.
- The solution URL overlaps other content in Findings.
Sensitive Data
New Features
- Richer sensitive data view — New stats on the sensitive data page, plus API type, newly-added, external, and trace context for each item.
- Improved PII detection using a new NER model alongside regex, and external flags surfaced in sensitive data.
Runtime Protection
New Features
- Replay-attack protection — Added nonce deduplication and token lifetime enforcement to defend against replay attacks.
- Added a health check for the Protection module.
Sensors & Deployment
New Features
- AWS ECS Fargate deployment — One-click deploy and enhanced installation scripts for the Satellite and PCAP sensor on AWS ECS Fargate, with updated task definitions.
- Zero-downtime key rotation for the Satellite — A new decryption pipeline with zero-downtime key-store rotation, a filesystem key store, and pluggable decryption scripts for Satellite traffic.
- eBPF sensor self-monitoring of CPU and memory, and a more efficient collector configuration with metrics export.
Resolved Issues
- An eBPF sensor memory leak, and poor eBPF sensor restart behavior.
- A Java agent memory leak and binary payload corruption.
Integrations
New Features
- Improved integrations page — A refreshed integrations experience in the dashboard.
- Keycloak LDAP/AD user federation for on-prem installations, LDAP support for multiple AD groups, and improved Auth0 subject detection.
- Chrome extension now captures application data.
Reporting & Compliance
New Features
- New report types — Added AI Agents reports, a change-log and auth-schema report, an environment test report, and an RBI compliance report integrated into the UI.
- Past Reports now show request metadata and offer filters; reports can be downloaded via secure links.
- Report storage moved to durable object storage and a database for reliability.
Resolved Issues
- Report numbers are incorrect.
Platform, Administration & Access
New Features
- Admin portal upgrades — New Environments tab, Feature Control, Session Management, org detail tabs, dark mode, and global API error handling with an error boundary page.
- Modernized authentication UI — Redesigned login and signup experience, with redirect back to your original URL after login.
- Sticky header rows, better empty-space handling on large screens, and the dashboard UI upgraded to a current runtime.
Resolved Issues
- Filters and cache do not reset on organization switch.
- The Test Plans page crashes when sorting.