Release Notes — May 2026

Release period: 2026-05-01 → 2026-05-31
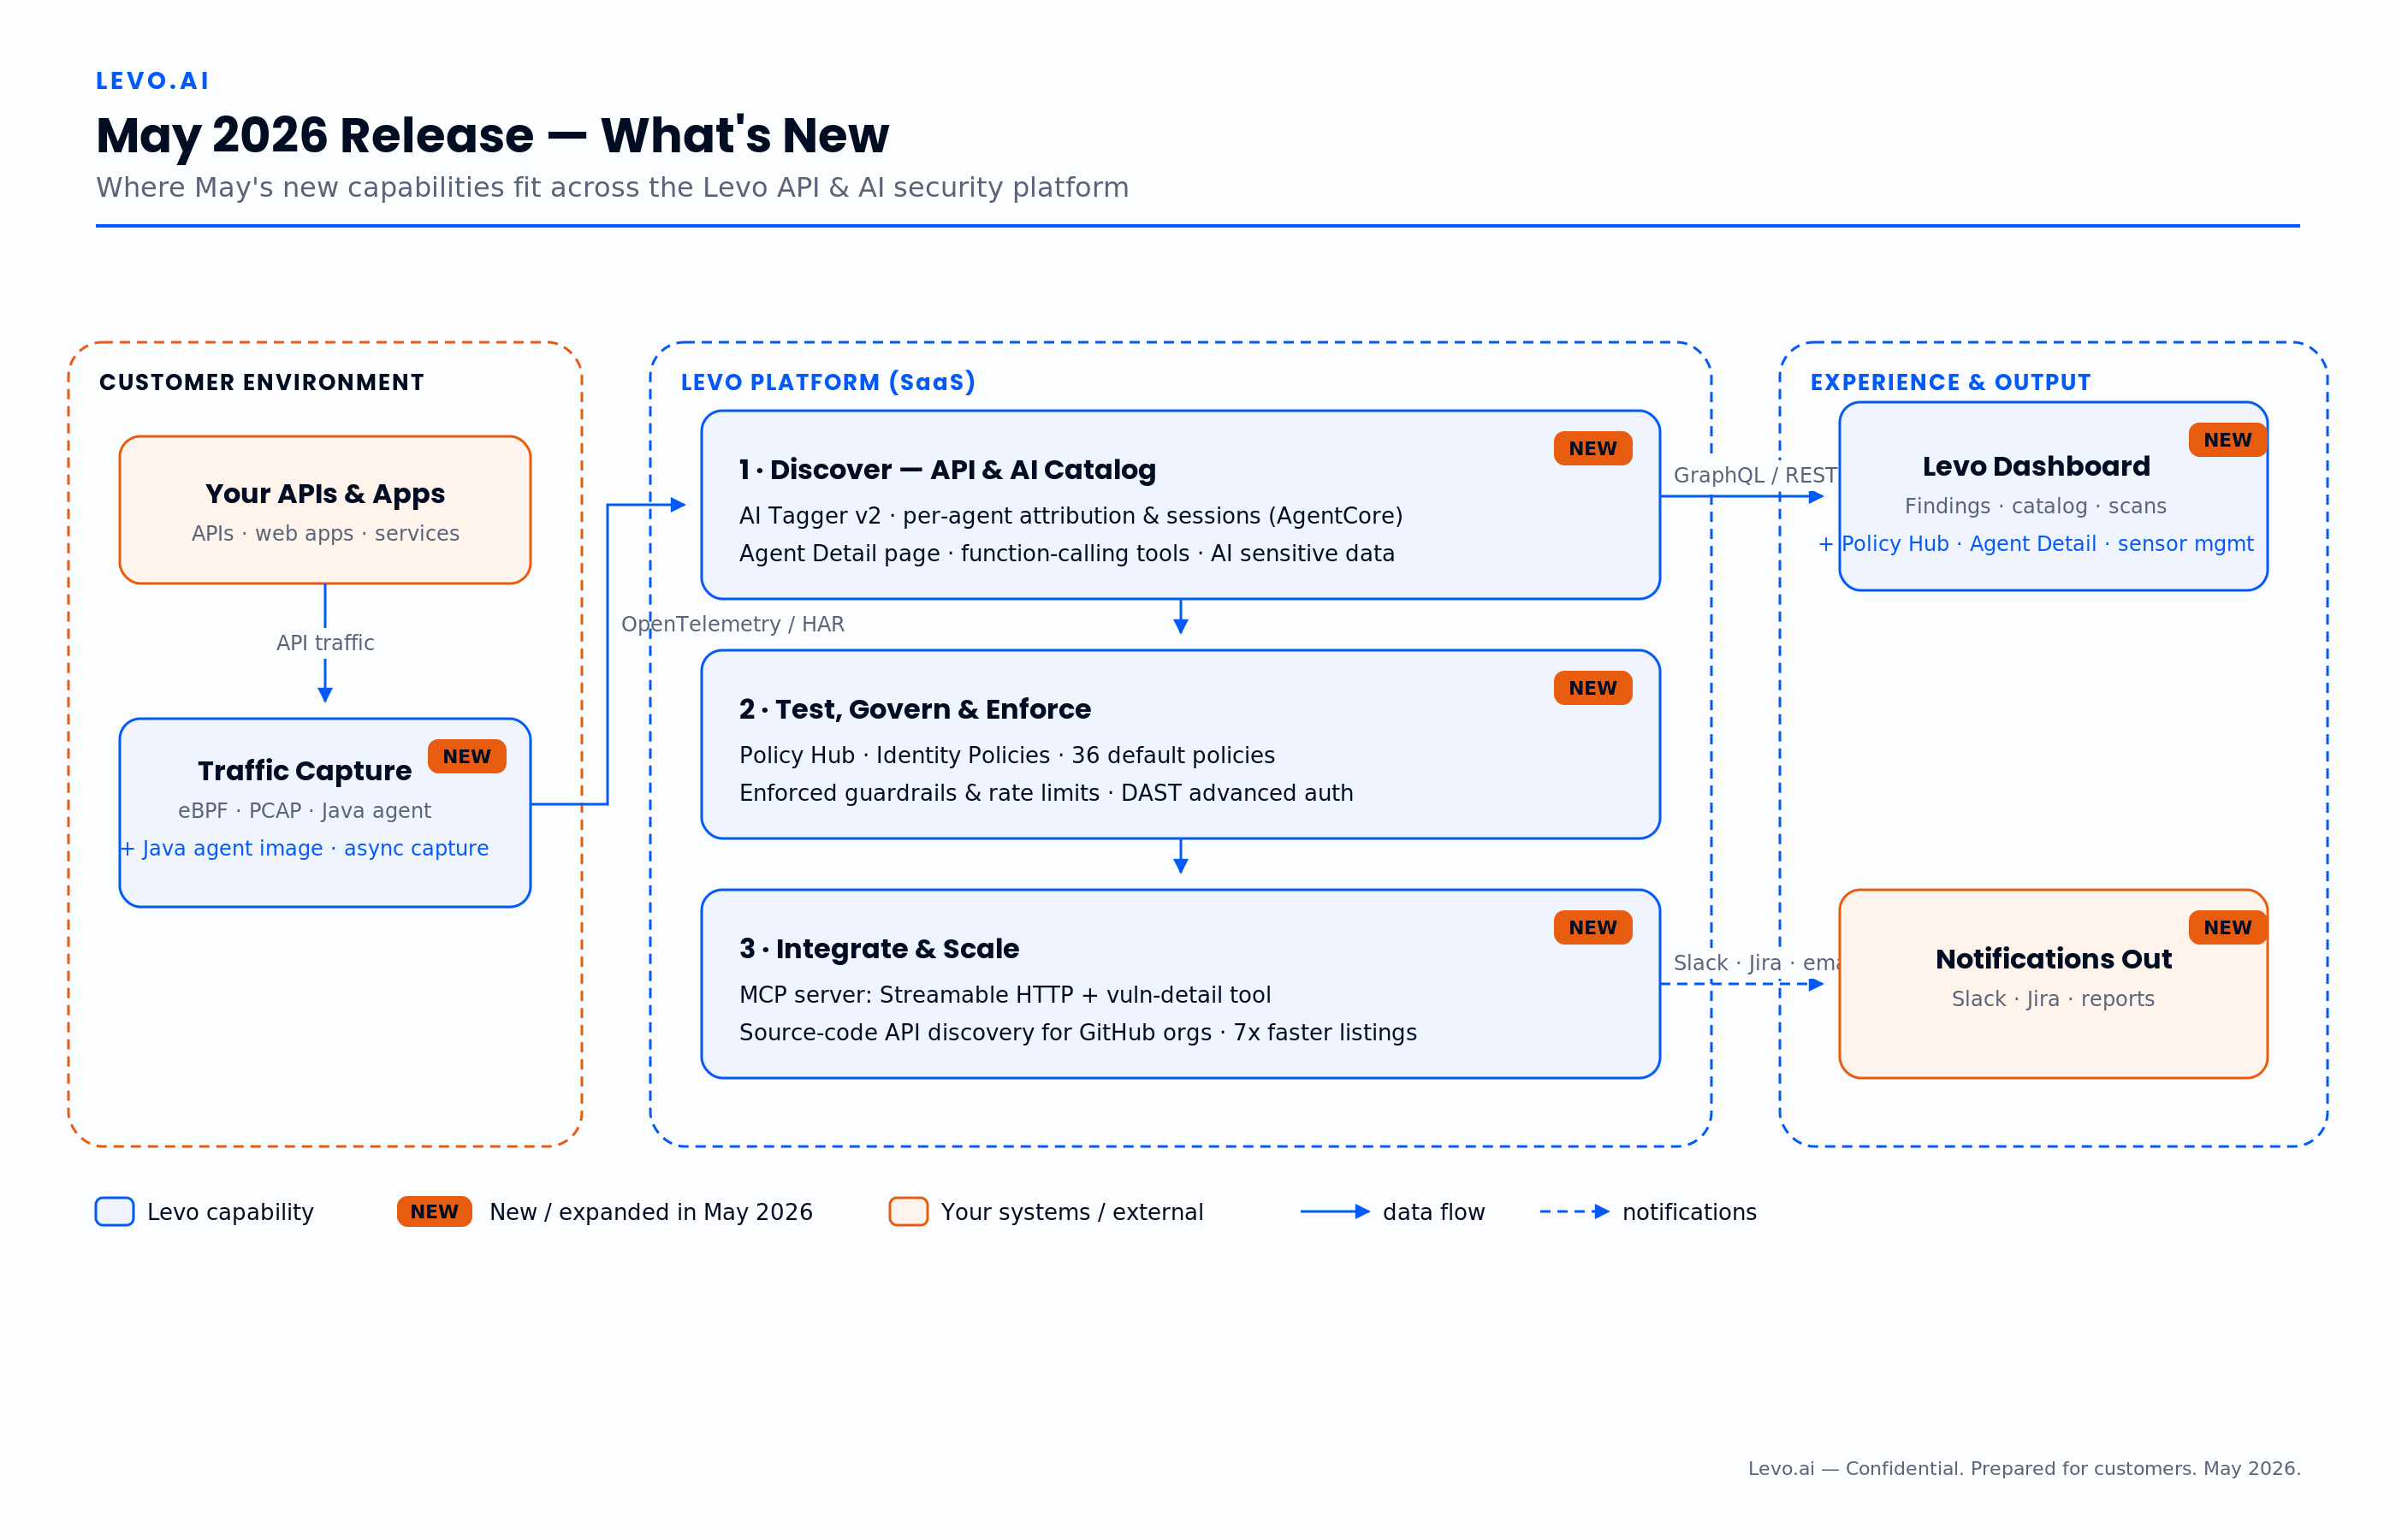
May deepens Levo's AI security stack: a redesigned Policy Hub with identity-aware policies, a next-generation AI traffic tagger that attributes traffic to individual agents and sessions, and a full Agent Detail view. We also added Streamable HTTP transport for the MCP server, deeper API discovery from source code, and broad reliability and performance gains across the platform.
Highlights
- Policy Hub with identity-aware AI policies — The AI Policies page is now a redesigned Policy Hub with inline Monitor/Enforce toggles, server-side pagination, and a new Identity Policy type that matches principals across clouds. Default policies expanded from 16 to 36.
- AI Agent Detail and per-agent attribution — A new Agent Detail page (Models, MCP, Tools, Findings, Traces) backed by a next-generation AI traffic tagger that attributes traffic to individual agents and reconstructs sessions, including AWS Bedrock AgentCore.
- MCP server Streamable HTTP transport — The Levo MCP server adds Streamable HTTP transport with header-based auth and new tools, including full vulnerability detail with HTTP traces.
- Enforced AI guardrails — The AI Gateway wires rate-limit policy actions to token-bucket enforcement, scans LLM response bodies, and enriches guardrail alerts with caller identity and policy lineage.
- Faster, more reliable platform — Up to 7x faster app and endpoint listing, plus extensive hardening against stalls, deadlocks, and trace drops.
- Discover more APIs from source — Source-code scanning now runs in parallel across entire GitHub organizations, with offline spec generation and large-repo controls, to surface APIs that may never appear in live traffic.
What's new at a glance. A one-page map of where May's additions land across the Levo API and AI security platform.
API Discovery & Cataloging
New Features
- Force-refresh OpenAPI spec — Manually force a refresh of an application's OpenAPI spec from the org details page.
- Discover APIs from source at scale — Source-code scanning now runs in parallel across entire GitHub organizations, with include/exclude directory controls for large repositories and an offline spec-generation mode, surfacing APIs that may never appear in live traffic.
- Endpoint and application reports now include tags, and applications show all source types when they have both observed traffic and imported endpoints.
- Source-code scanning skips unsupported languages, classifies empty-spec outcomes, and ignores node_modules and build directories.
Resolved Issues
- Endpoint renames fail silently.
- Environment filtering for application listing does not work correctly.
- Soft-deleted environments cannot be revived reliably.
- Storage-version mismatches and dependency errors in the .NET source-analysis path.
API Security Testing
New Features
- AI-authored tests (early access) — New scaffolding and validation APIs for AI-authored tests, with a persisted plan and approval state machine, and test execution gated behind approval status.
- Exported test plans now produce a runnable zip, and test results are richer with real-time streaming.
Resolved Issues
- False positives and weak detection for OS command injection and input validation.
- LFI tests mishandle empty response bodies.
Web Application Scanning (DAST)
New Features
- Advanced authentication strategies — DAST scans add opt-in multi-step DOM-driven login, session-transplant and storage-state strategies, and static MFA pass-through, plus an iframe-aware login resolver for Keycloak, Auth0, and Okta SSO.
- Redesigned Create DAST Scan modal — A cleaner scan-creation experience, with the option to run scans on Levo Cloud or on-prem.
- Time-based SQLi detection with N-sample confirmation, and improved crawler diversity.
Resolved Issues
- High false-positive rates across passive and active scanners — reduced by up to ~75% on some paths.
- DAST scan creation is allowed when the feature flag is disabled.
AI Security
New Features
- Policy Hub with Identity Policies — The AI Policies page is redesigned as a Policy Hub with an Identity Policy editor, inline Monitor/Enforce toggles, and server-side pagination. A new Identity Policy type matches principals across clouds, and default policies expanded from 16 to 36, seeded automatically for new environments.
- Enforced guardrails and rate limiting — The AI Gateway wires rate-limit policy actions to token-bucket enforcement, scans LLM response bodies for output policies, and supports hot-reload policy enforcement via a new control plane.
- Richer guardrail alerts — Alerts now carry caller identity (source address, IAM principal, user agent, model, upstream), policy lineage, real scanner names, and gateway-supplied titles, with enforcement mode following the originating policy.
- Azure OpenAI native passthrough for transparent API-key forwarding, plus guardrail model cache pre-warming and reduced gateway memory usage.
Resolved Issues
- Guardrail alerts are not written to a dedicated alerts table.
- Scanners fire more than once for the same event.
AI Discovery
New Features
- Next-generation AI traffic tagging — A new AI Traffic Tagger attributes traffic to individual agents and sessions, recognizes AWS Bedrock AgentCore runtime callers, and adds A2A discovery and comprehensive AI-provider parsers.
- Function-calling tools and AgentCore identity — Discover function-calling tools alongside MCP tools, with per-agent identity from AgentCore, and support for server-less MCP tool rows.
- AI and MCP trace ingestion and querying via a trace-type filter, with a Trace Type switch on the Traces page and PII type names shown inline in the Findings table.
Resolved Issues
- MCP entities are modeled incorrectly when captured at the proxy or gateway.
- Per-agent attribution is incorrect, and agent identifiers are unstable across batches.
Vulnerabilities & Findings
New Features
- Persistent filters — Vulnerability filters are retained across list and detail views.
Resolved Issues
- Auto-closing a vulnerability on a flagged endpoint omits your comment.
- Bulk vulnerability updates are not processed reliably.
Sensitive Data
New Features
- Sensitive data findings for AI workloads — New sensitive-data finding services with entity-type awareness, and PII data pivoted to AI-aware entities so findings cover AI agents and sessions.
- Entity type is now included across all sensitive-data APIs.
Runtime Protection
New Features
- Protection module health check is now enabled by default.
Sensors & Deployment
New Features
- Java agent published to a public container registry — The Java agent is now available as a published container image.
- Higher-throughput, self-diagnosing capture — The Java agent adds an async dispatcher with sampling, connection-level sticky sampling, host/port filters, TCP 5-tuple recovery across Tomcat, Jetty, Netty, and Vert.x, per-endpoint rate limiting (dark-launch), and self-diagnosing capture for third-party APIs.
- The eBPF sensor adds richer socket-info capture and preserves in-progress request data, with noisy health probes suppressed at the capture layer.
Resolved Issues
- Silent capture loss and over-capture on Java 8.
Integrations
New Features
- Slack notifications — Levo can now send notifications to Slack.
Resolved Issues
- User organization invitations fail.
- Unaccepted org invites appear in the org picker.
Reporting & Compliance
New Features
- New reports added and page-size handling improved, with a wider Actions column to fit Preview and Download buttons.
Resolved Issues
- Report pagination and download issues.
MCP Server
New Features
- Streamable HTTP transport — The Levo MCP server adds Streamable HTTP transport at /mcp with header-based authentication.
- Full vulnerability detail tool — A new MCP tool returns full vulnerability details including the complete HTTP trace, alongside additional test-authoring tools.
Platform, Administration & Access
New Features
- Polished on-prem sensor management — The Sensors page adds status pills, a Type column, search, compact layout, and contextual empty states, plus a Deployments and Configuration tab.
- Faster listings — App and endpoint listing is up to 7x faster thanks to new indexes, with broad hardening against stalls, deadlocks, and trace drops for a more reliable experience.
Resolved Issues
- Expired sessions are not handled gracefully. A one-shot token refresh now applies, and benign auth-page network errors are quieter.
- Application name changes do not reflect in filter dropdowns across modules.
- Stale JavaScript chunks cause load failures.